



Vulnerability Researcher
Thales · Internship
I’m Simon Robin, also known as sljrobin. I find attack paths in cloud-native infrastructure and platforms, as well as Kubernetes clusters, and I help the teams who run them close those gaps by design.
I’m always glad to talk about security. You’ll find me on several networks, but LinkedIn is where I usually answer.
I’ve done offensive security for over 10 years, testing web and mobile applications, assessing networks, and building threat models. Today, I specialize in cloud security. Recently, I created the Kubernetes testing methodology my firm uses, and I’m turning to AI as a tool to find and explore new attack paths.
In the following lines, I tell how a worm got me into security, where I’ve worked and studied, and what I do off the clock.
Security found me during a summer in high school. A file called autorun.inf, which looked legitimate, kept appearing on my USB sticks and hard drives. Later, I found it strange that my antivirus couldn’t fetch its updates. After days of reading forums about this behavior, I finally understood what had happened: the Conficker worm had infected my machine. One question remained. How, despite everything I had done to protect it?
This puzzle pulled me into the field. I wanted to understand how things worked under the hood. Security was already vast and specialized, and I was eager to start learning.
I decided to go to ESIEA, a French engineering school, to prepare for a career in security. I chose it for its recognized Cryptology and Virology lab, which I was lucky to join as a student. There, I studied the security of bootloaders and the arrival of UEFI, the firmware interface that was replacing the BIOS.
The curriculum was heavy on mathematics and physics, which I loved, and some quantum physics and electronics. The computer classes were the ones I enjoyed the most. We learned to code in C, studied algorithms and their complexity, and touched on network security and cryptography.
During those years, I also completed two internships: one at Airbus as a software engineer, the other one at Thales as a vulnerability researcher, where I discovered the field of fuzzing.
Outside school, I started writing small programs, mostly in Python. I still do, and I share some of them on GitHub when I think they might help someone.
In addition, I began playing capture the flag (CTF) challenges. OverTheWire was my playground at first. Later, I played in a team with friends.
When I have the time, I still solve challenges on Root Me, NewbieContest, and WeChall. I enjoy learning advanced attacks. For the web, my go-to place is PortSwigger’s Web Security Academy, and for the cloud, I like to play the Wiz CTFs.
After I completed my MSc in Computer Science at ESIEA in 2015, I moved to the United Kingdom for a more advanced course in security. By then, the field had become a passion. I joined Royal Holloway, where I graduated with a second MSc, in Information Security.
In 2016, I moved to London and joined IOActive as an associate consultant. I felt lucky to be part of this company, and even luckier when I was allowed to study a topic of my choice at Imperial College London. I chose Chromium’s JavaScript bindings because browser security interested me.
Today, I’m grateful to have a job where I do offensive security and application security (AppSec) for a living.
Within the company, I grew and got to know some of the major areas of penetration testing, including web, network, mobile, red teaming, and threat modeling. Each area interested me, but I enjoyed iOS security the most. Exploiting the latest jailbreaks and using Frida with Objection to explore the memory of apps became a fascination.
Then, I got into cloud security, mostly by accident. I had the feeling that the field came down to configuration reviews, but the area is vast, and the complex attack scenarios caught my attention. Instead of getting administrative privileges on a machine, it was possible to disrupt a whole company. I’ve worked in this area for a while now, and I enjoy it as much as on the first day.
Now, AI is changing my perception of the field. Agents, the exploitation of large language models, and platform security bring new challenges and exciting new opportunities.
IOActive · Full-time
Thales · Internship
Airbus Defence and Space · Internship
ESIEA Operational Cryptology and Virology Lab · Part-time
All my badges can be verified on the following platforms.
A hands-on workshop on attacking Kubernetes clusters, from a compromised workload up to the cluster itself, and on building them so that the same attacks fail.
Four days of attacking and then securing AWS, Azure, and GCP in a lab, from storage and identities to serverless and containers, each flaw with its fix.
A one-week course in Stuttgart on Daimler’s threat modeling and security architecture practice, with an exam at the end.
The Cisco Networking Academy’s four modules over two summers, from network fundamentals to routing, LAN switching and wireless, and wide area networks, each with its labs.
Focused on Chromium browser security, developing techniques to automate the discovery of bugs in JavaScript bindings.
Royal Holloway, University of London
Specialized in security testing, software security, network and computer security, cryptography, and digital forensics.
French engineering school (diplôme d’ingénieur), majoring in information security.
When I’m not behind a laptop, I enjoy doing other things: I play music, I take pictures, and I build a few projects with LEGO.
Music is an old love of mine, and a precious one. I started playing the piano when I was 3. Putting notes together has always come naturally to me, probably because I was born with perfect pitch. I joined the Bordeaux Conservatory, where I studied classical music for a few years.
I played Romantic pieces by composers such as Schubert, Schumann, and Chopin, but the musical genius who moved me the most was, without a doubt, Beethoven.
Around 2006, I switched to the electric guitar. After two years at a music school, I decided to teach myself the bands I was listening to at the time, mostly AC/DC for the groove and Dire Straits for the melodies. My tastes changed over the years but stayed close to the blues. Like many before me, I was intrigued by Robert Johnson, then by John Lee Hooker, Doc Watson, J.J. Cale, and B.B. King, not to mention Eric Clapton and Jeff Beck.
I own an Epiphone SG that I’ve modified from the headstock to the pickups, and a Gretsch Vintage Select ’62 Jet. I use the Epiphone with light strings for solos, whereas the Gretsch is dedicated to riffs. Like Malcolm Young, I string it .012 to .056 with a wound G.
And I’ve always hoped my neighbors share my love of music.
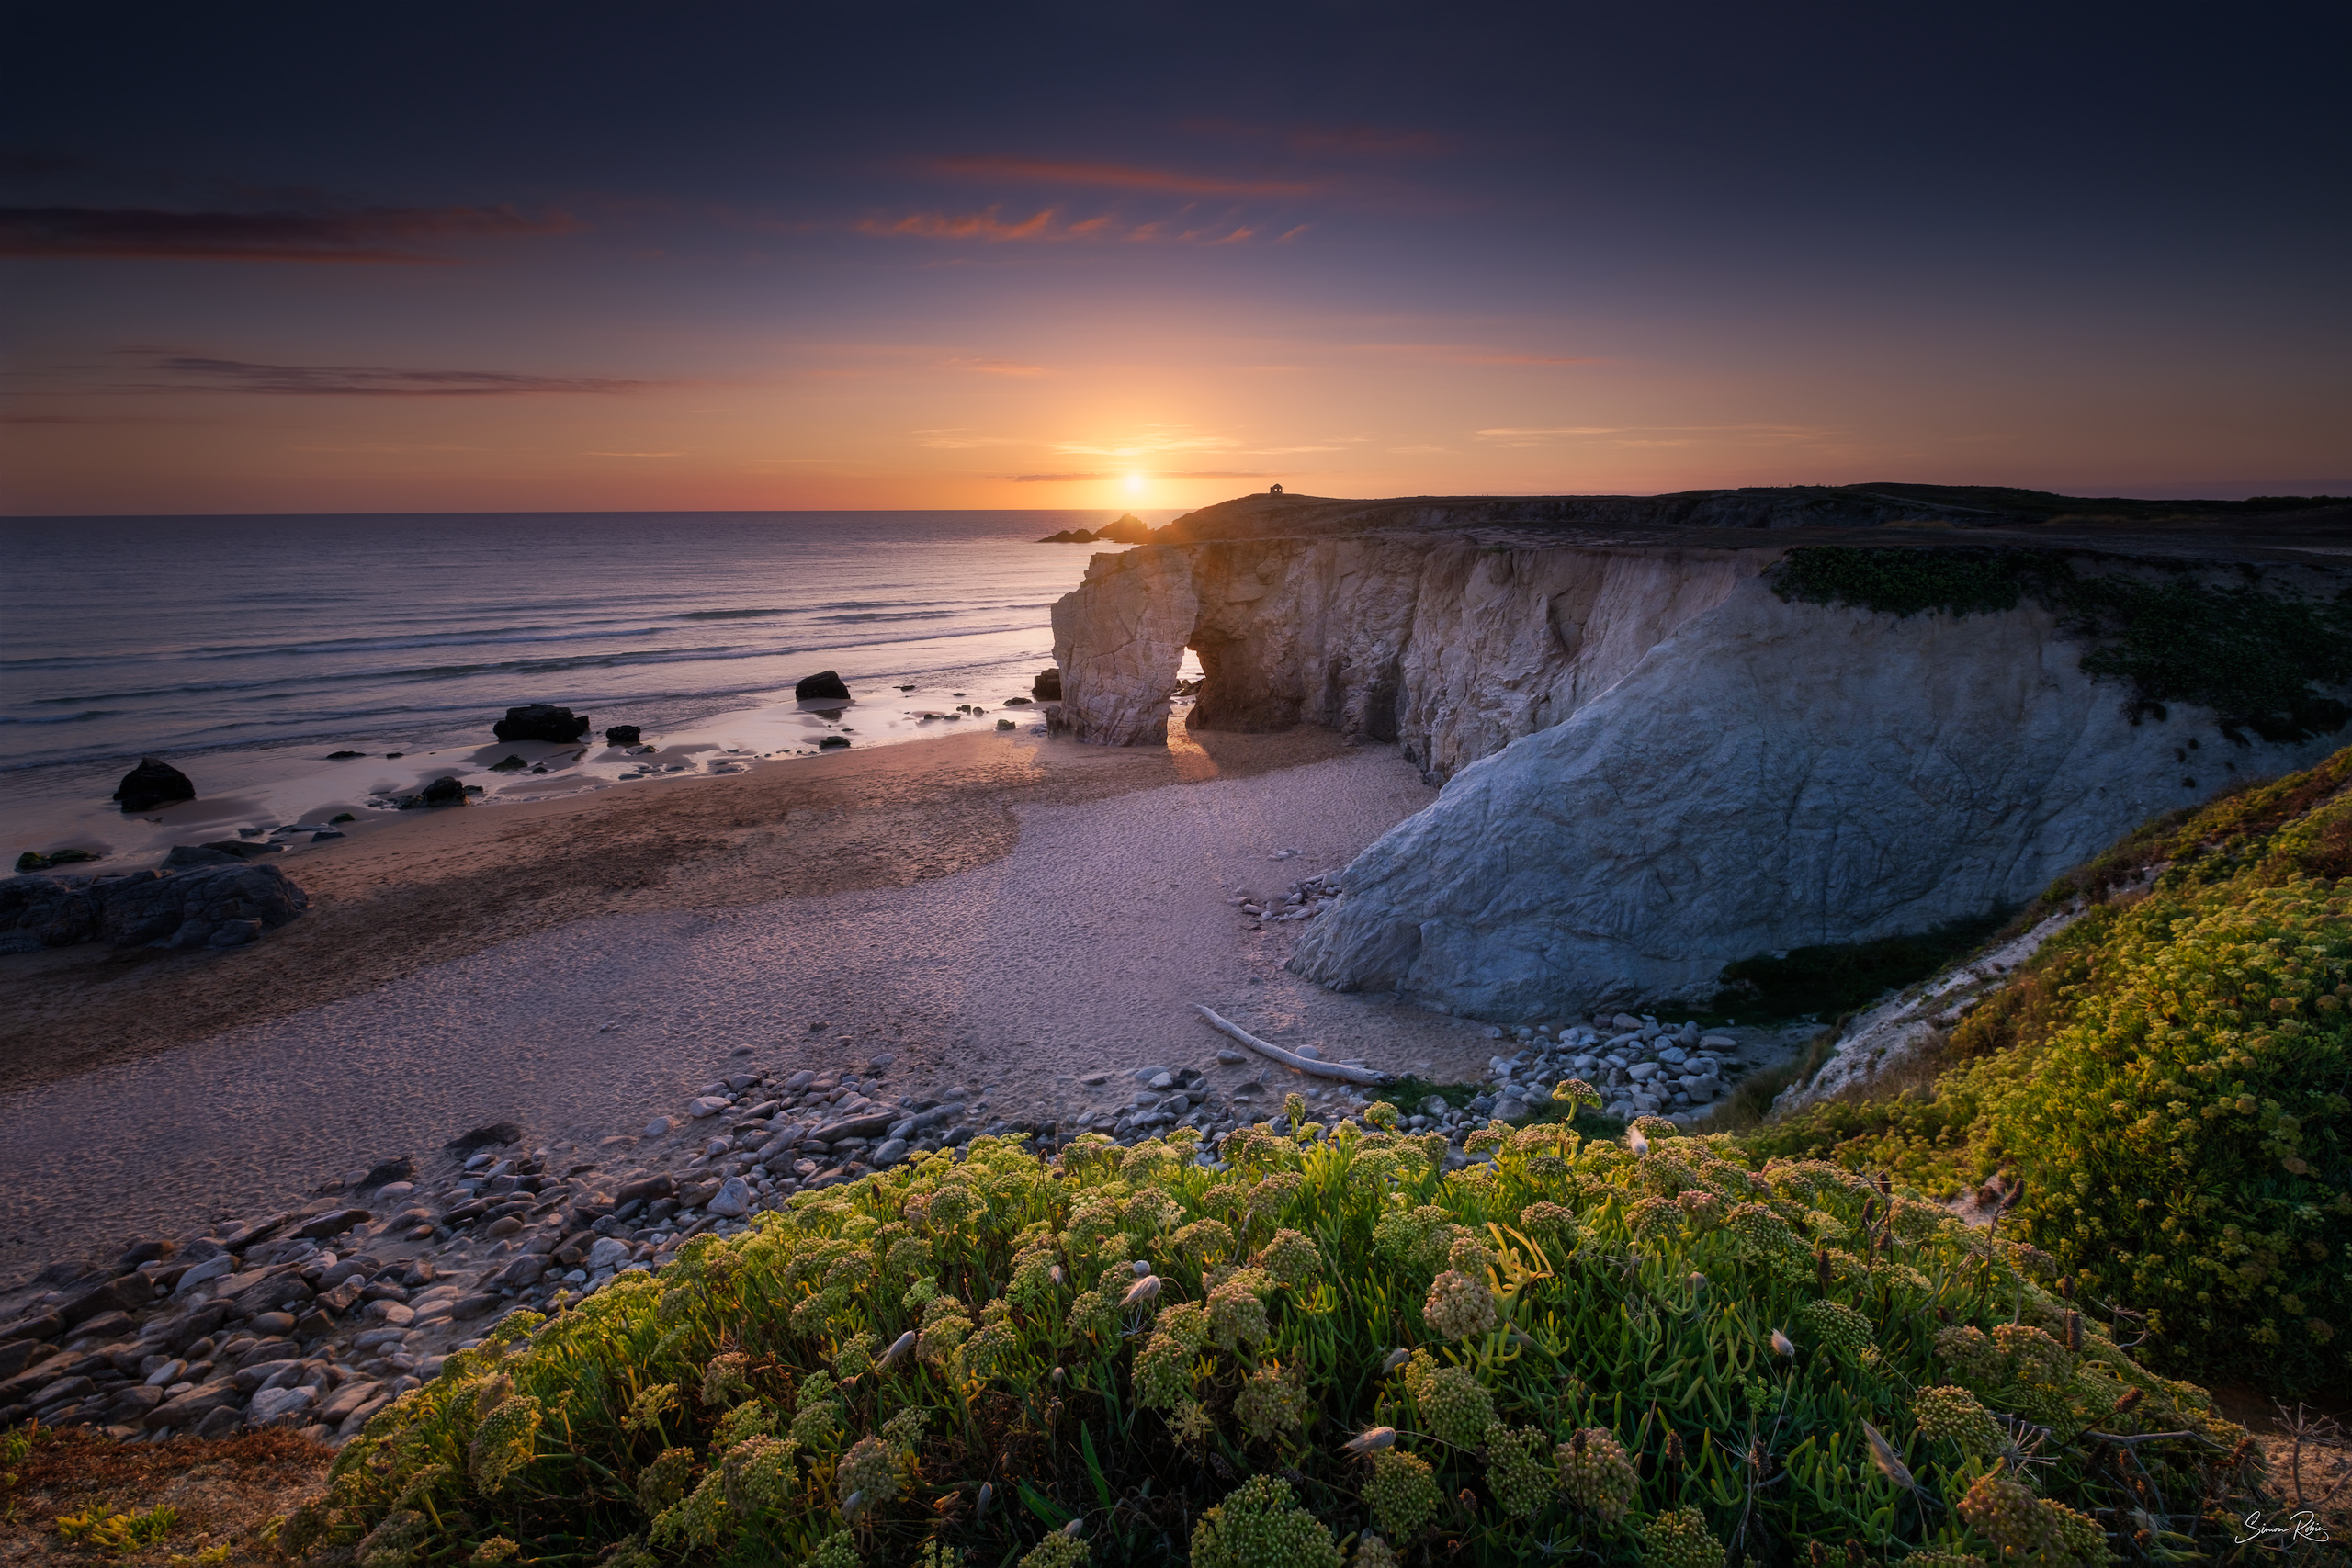
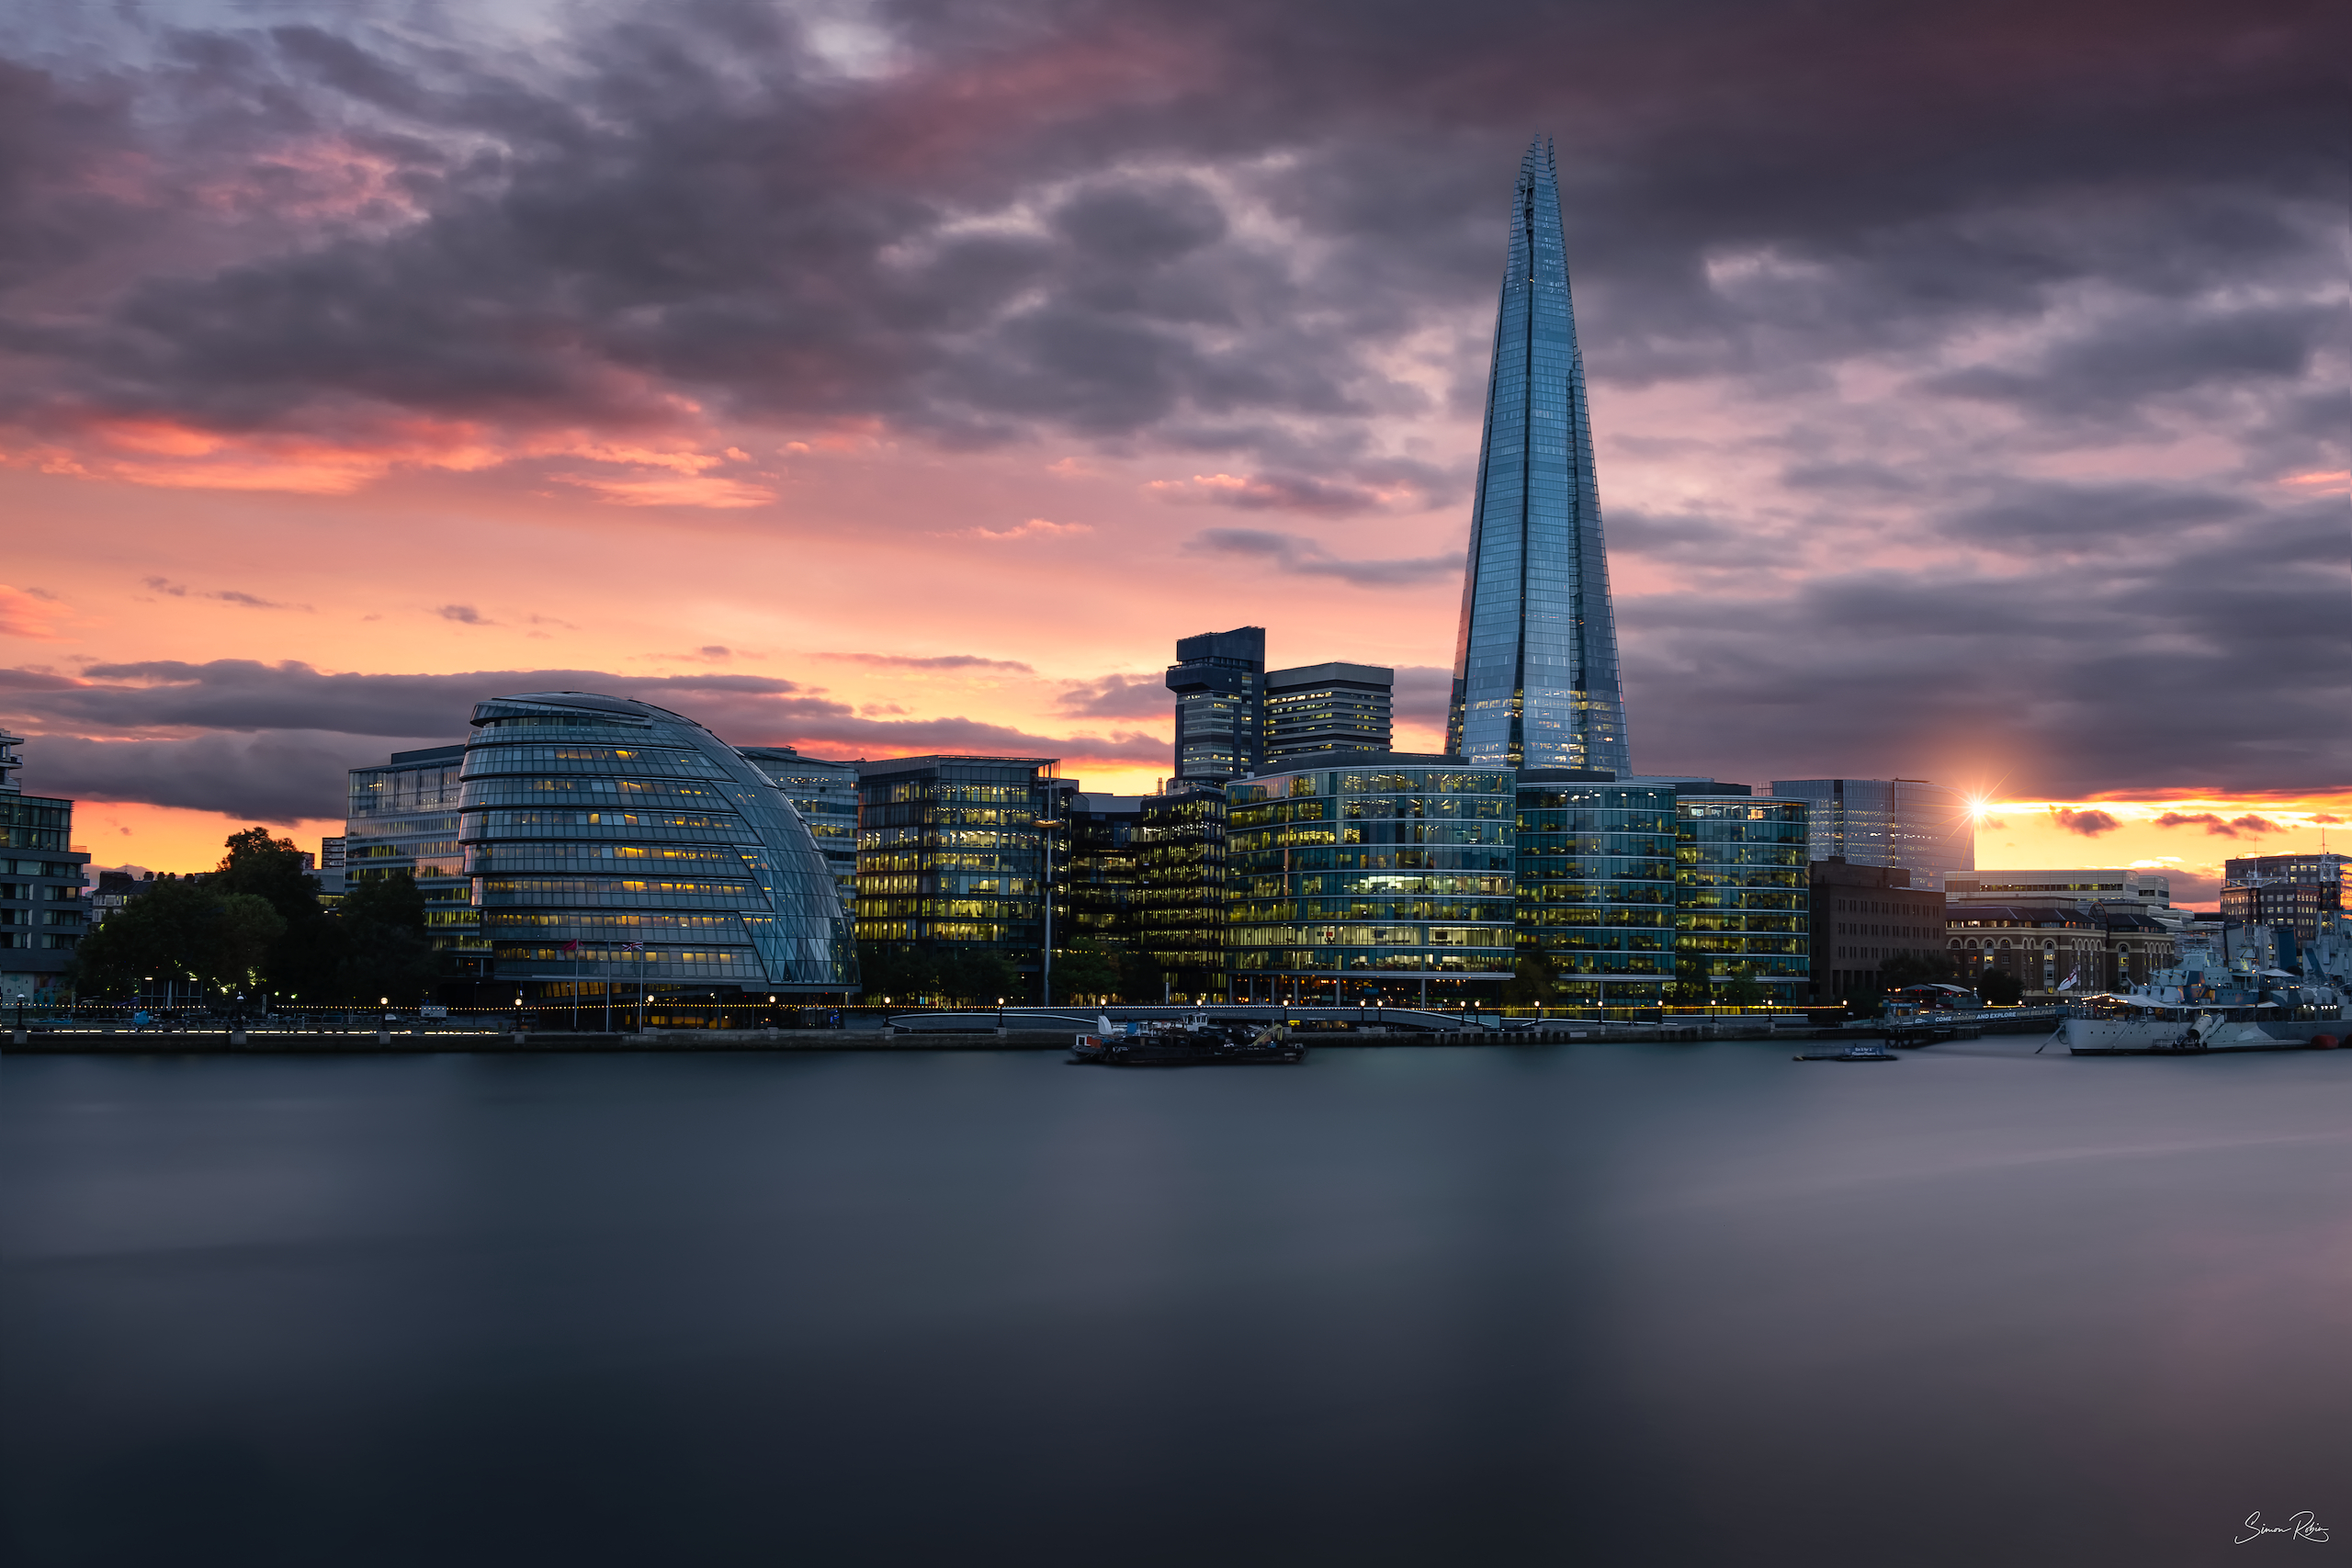
Going out to take pictures is another passion of mine. I enjoy chasing the light and admiring nature.
I started in 2017, before a trip to Seattle. Like music, I found it demanding, sometimes thankless, and a teacher of patience. Waking at 4 AM, walking to the spot, setting up the camera on its tripod, and waiting for the sun, only to get a covered sky and flat light, can be frustrating. Trying again and again eventually gives a beautiful picture, and the reward is worth the early mornings. I shoot mostly cityscapes and landscapes.
Some of my pictures are in the Photography section, and the stories behind them are on Behind the Camera.
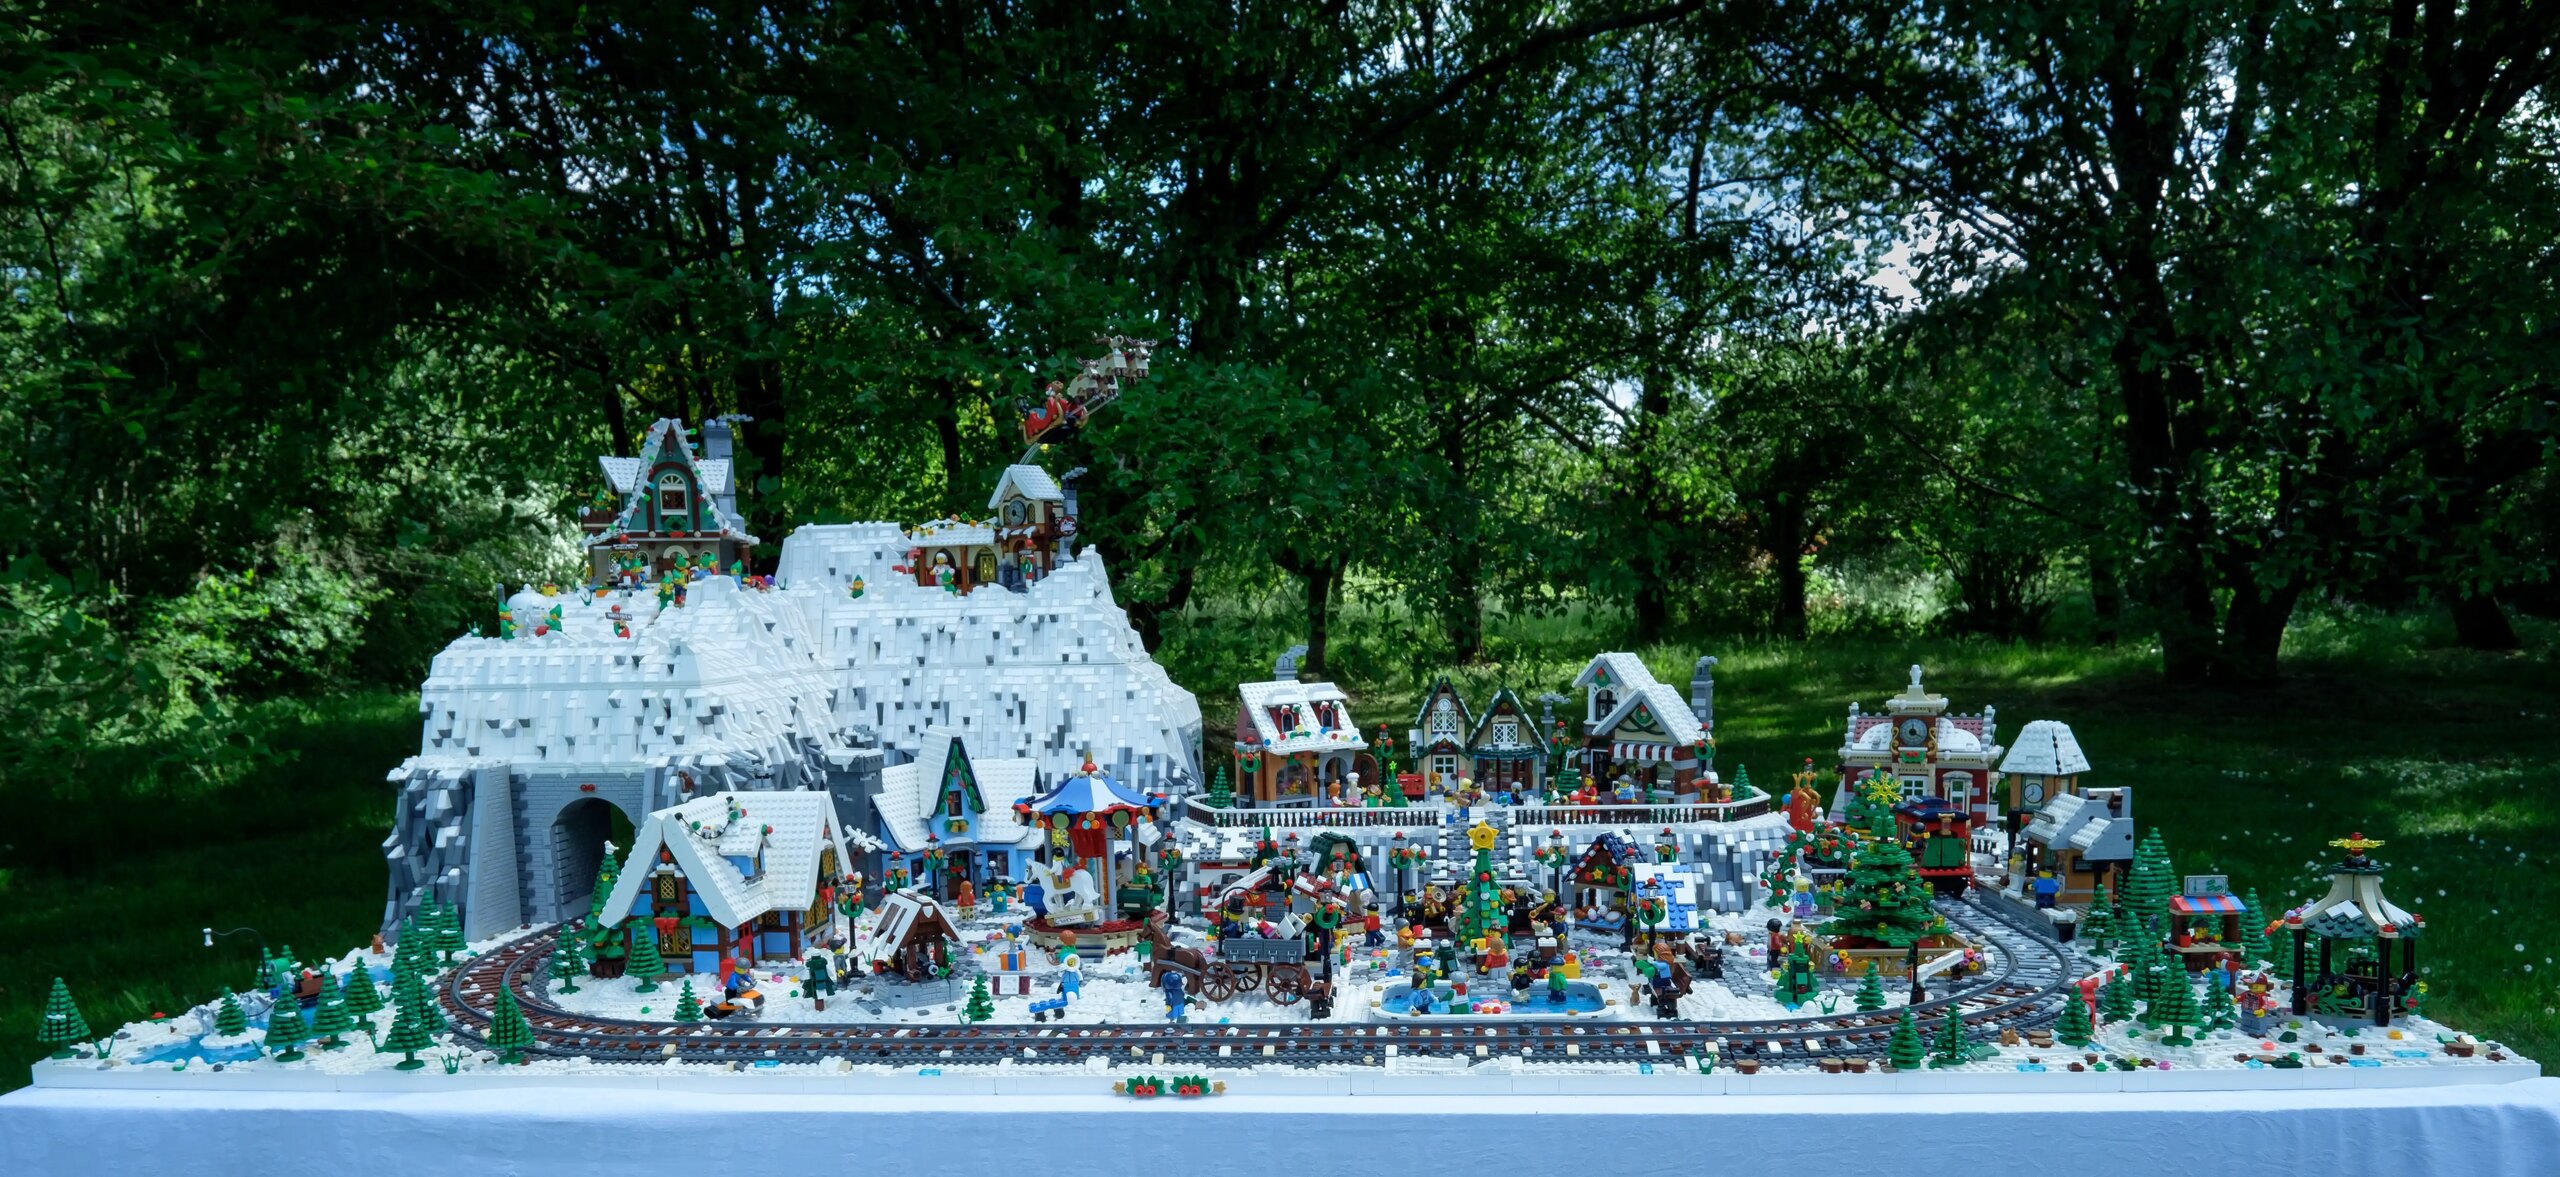
The last of my hobbies is the oldest. I’ve built with LEGO since I was a kid, and the habit never left me. In December 2019, my family and I founded Brick Winter Burrow, a modular winter village. We built its foundations during the 2020 lockdowns, and we have never stopped improving it since.
This project lets me put the engineer’s hat back on, as I have to answer questions such as how to transport the buildings without breaking them, how to store the village, how to make the structures strong enough, or how to handle the weight. A 13 kg mountain brings its own risks.
I share what we learn on a blog for the AFOL community, the adult fans of LEGO. I write mostly about motorization, such as our switch to 9V, how to maintain and automate that system, and about electrification. For the latter, we developed a solution to replace cables using pogo pins, which lets us light streetlamps and buildings without dealing with wires.
The Brick Winter Burrow members also joined Brick Team Aquitaine, a club of LEGO fans. With some of its members, we travel to events in France on a regular basis to raise money for charities such as the Téléthon and the Secours populaire français.
I’m always glad to talk about security. Feel free to reach out at any of the following places, in the open or, with my PGP key, in confidence.
CREST has issued digital badges since 2024.1 Certifications passed before then carry none, and CREST doesn’t issue them retrospectively.2 The two CREST badges above stand for the certifications; no CREST badge was issued to me.